Wi-Fi employee access – Fortinet
In this topic, you will learn how to configure FortiGate firewalls with FortiAP access points to authenticate Wi-Fi devices with Portnox™ Cloud using 802.1X, 802.1X over RadSec, MAC-based authentication, and identity pre-shared keys (IPSK).
FortiGate with FortiAP
In this section, you will learn how to configure a FortiGate firewall and the FortiAP access points that it manages to work together with Portnox™ Cloud.
Add a RADIUS server
In this section, you will add a Portnox™ Cloud RADIUS server to the FortiGate using the CLI. You will use this server later when you configure your SSIDs.
-
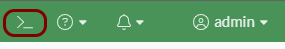
In the FortiGate web interface, click on the >_ icon in the top-right corner to open
the CLI console.
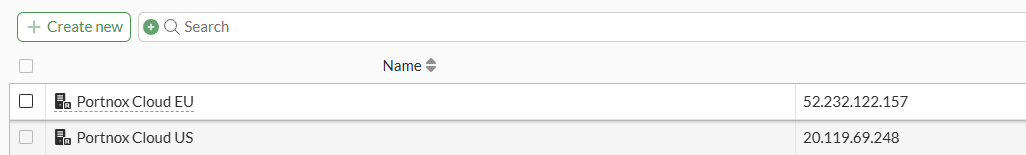
Result: The Portnox Cloud server appears in the FortiGate web interface, in .
Optional: Add a RadSec server
Add a server for one-way RadSec
In this section, you will add a server that connects to the Portnox Cloud RADIUS server using RadSec.
Before you begin, in Portnox Cloud, go to , select the relevant RADIUS instance, and select . Activate the Enable RADIUS over TLS (RadSec) option, disable the Validate NAS Client Certificate (RadSec) option, and click on the Save button.
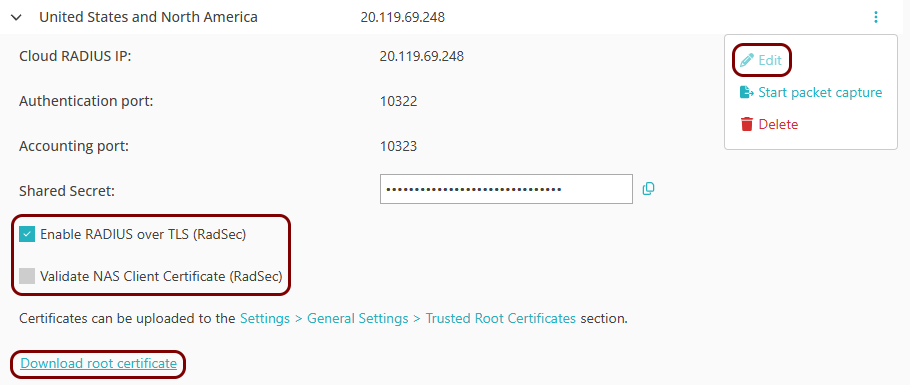
The FortiGate includes the DigiCert Trusted Root G4 certificate of the Cloud RADIUS servers by default, as
DigiCert_Trusted_Root_G4. You do not need to download or import it.
-
In the FortiGate web interface, click on the >_ icon in the top-right corner to open
the CLI console.
Result: You added a RadSec server. When you configure an SSID, select this server instead of the non-RadSec server.
Optional: Configure mutual authentication (mTLS)
In this section, you will configure Portnox Cloud to verify the certificate of the FortiGate during the RadSec connection.
During the RadSec connection, the FortiGate presents a factory certificate signed by the Fortinet certificate authorities. In this section, you configure Portnox Cloud to trust these certificate authorities. As a result, Portnox Cloud trusts the factory certificate of any Fortinet device, not only your FortiGate.
To limit trust to your own devices, create your own certificate authority and use it to sign a client certificate
for the FortiGate. Then, import this certificate on the FortiGate, select it with the set
client-cert command in the RadSec server settings, and upload your certificate authority to Portnox
Cloud instead of the Fortinet certificate authorities.
-
In the FortiGate web interface, in the left-hand side menu, select the option.
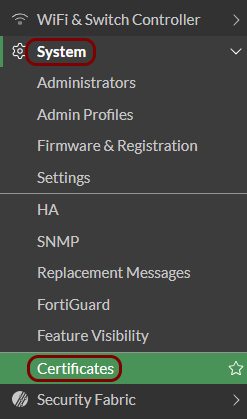 Note:If you do not see the Certificates option, select the option, activate the Certificates option, and click on the Apply button.
-
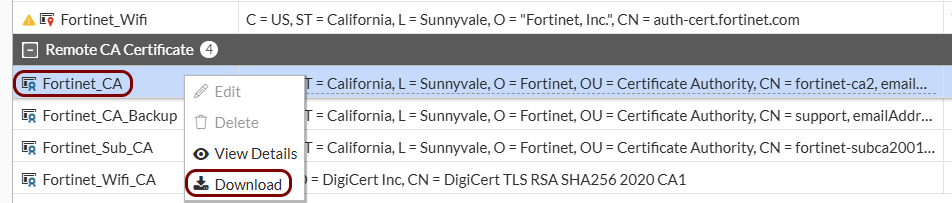
In the Remote CA Certificate section, right-click on the row representing the
Fortinet_CA certificate to open a context menu, and click on the
Download menu option.
-
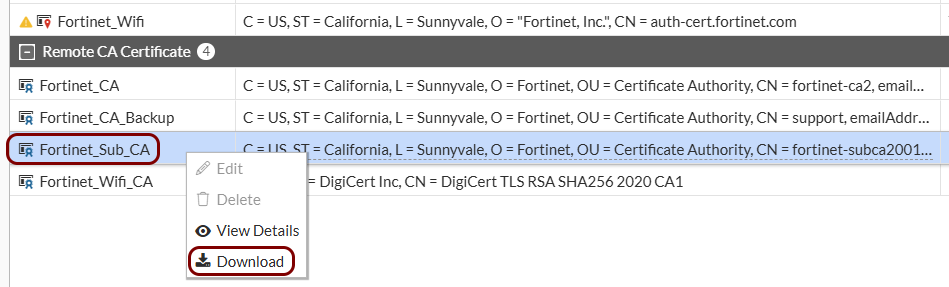
In the Remote CA Certificate section, right-click on the row representing the
Fortinet_Sub_CA certificate to open a context menu, and click on the
Download menu option.
-
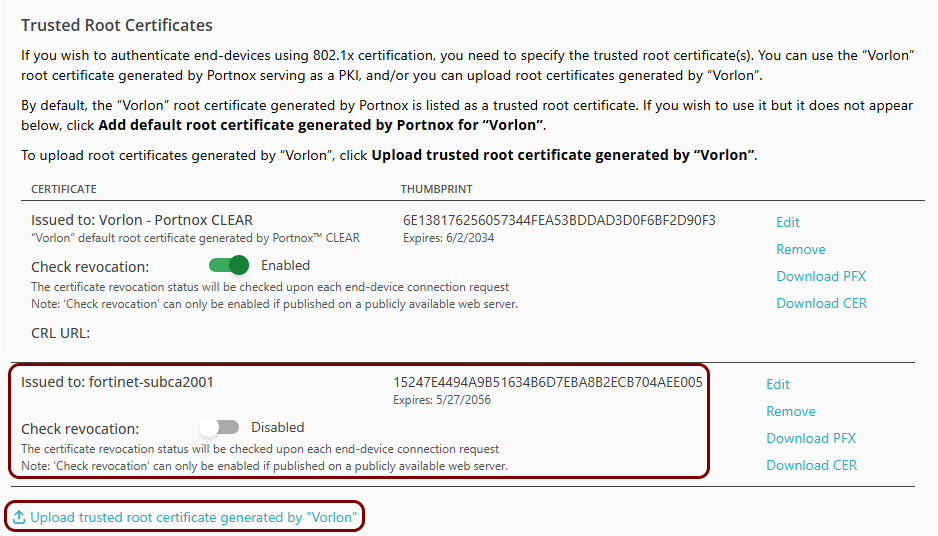
In Portnox Cloud, go to , and upload the Fortinet_CA_chain.pem file.
-
Go to , select the relevant RADIUS instance, select , activate the Validate NAS Client Certificate (RadSec) option, and
click on the Save button.
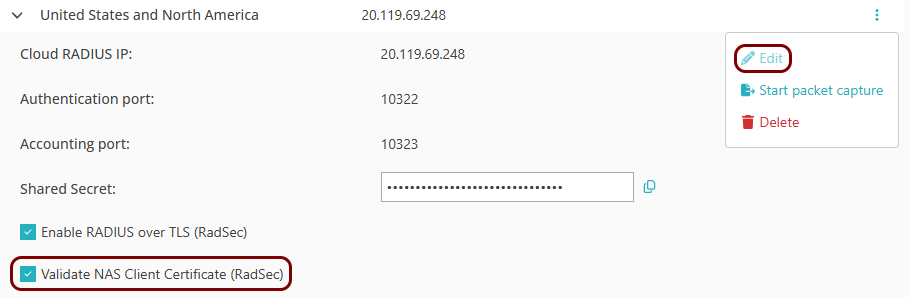
Result: The FortiGate and Portnox Cloud authenticate each other when the FortiGate connects using RadSec. The RadSec server and the SSIDs that use it need no changes.
Create an SSID for 802.1X authentication
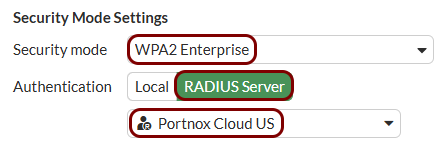
In this section, you will create an SSID and configure it for WPA2 Enterprise authentication, using the RADIUS server that you created earlier.
-
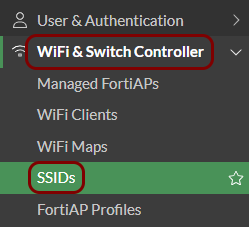
In the FortiGate web interface, in the left-hand side menu, select the option.
-
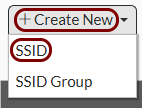
Click on the Create New button, and select the SSID option.
-
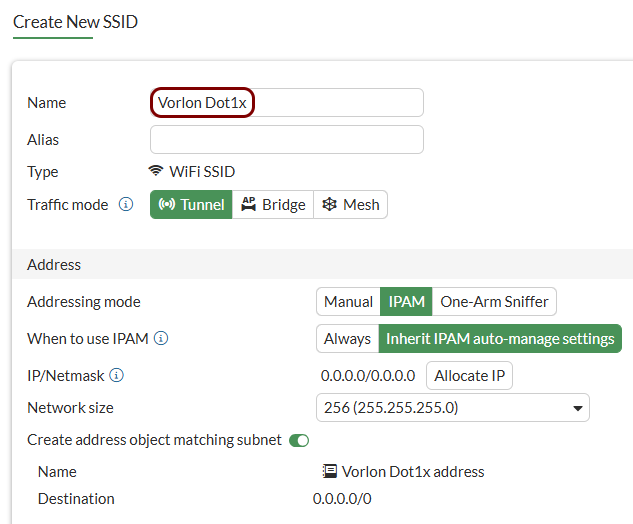
On the Create New SSID screen, configure the general settings:
-
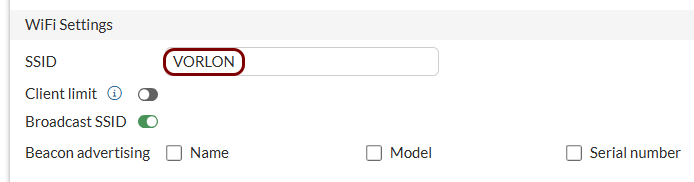
In the WiFi Settings section, in the SSID field, enter the
network name that devices see when they search for Wi-Fi networks.
-
In the Security Mode Settings section:
-
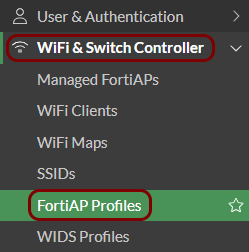
In the left-hand side menu, select the option.
- Optional:
Make sure that your access points broadcast the SSID:
-
Check the SSIDs column of the profile that your access points use.

If the column shows All Tunnel Mode SSIDs for each radio and you selected the Tunnel traffic mode, the access points broadcast the SSID automatically. In this case, skip the next step.
-
Otherwise, double-click the profile. For each radio, in the SSIDs field, select
the Manual option, and select the SSID that you created. Then, click on the
OK button.
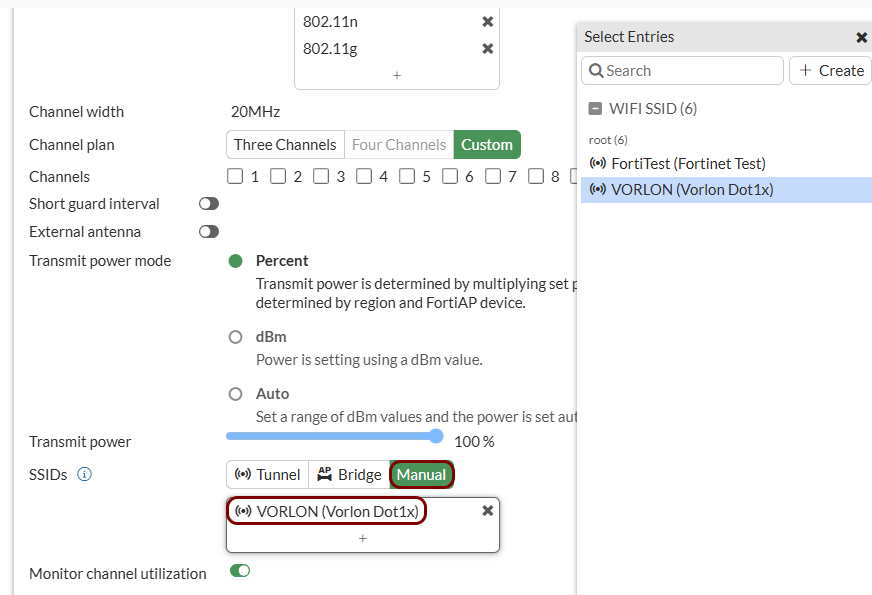 Note:The Manual option replaces the automatic list of SSIDs. Also select all other SSIDs that the radio must broadcast.
-
Check the SSIDs column of the profile that your access points use.
Result: You created an SSID that authenticates employee Wi-Fi devices using 802.1X and the Portnox Cloud RADIUS server.
Create a firewall policy
In this section, you will create a firewall policy that allows traffic from the SSID to other networks. Without this policy, Wi-Fi devices authenticate and connect, but they cannot reach any other network.
-
In the left-hand side menu, select the option.
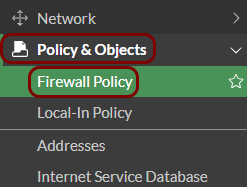
-
Click on the Create new button.
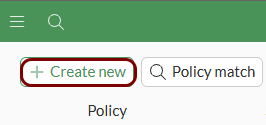
-
On the Create New Policy screen, configure the policy:
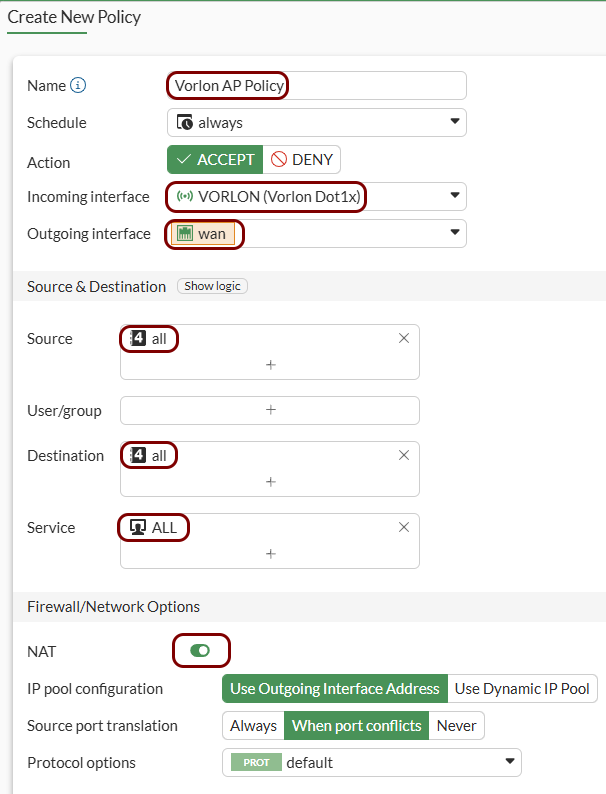
- In the Name field, enter a name for the policy.
- In the Incoming interface field, select the SSID that you created.
- In the Outgoing interface field, select the interface that connects the FortiGate to the internet, for example, wan.
- In the Source field, click on the + icon, and select the all option.
- In the Destination field, click on the + icon, and select the all option.
- In the Service field, click on the + icon, and select the ALL option.
- Leave the NAT option activated.
Result: Wi-Fi devices connected to the SSID can reach the internet.

Optional: Create an SSID for MAC-based authentication
This is an optional task. Follow this task only if you want to authenticate devices, such as IoT devices, that do not support 802.1X, using their MAC address instead. Skip this task if you do not need MAC-based authentication.
-
In the FortiGate web interface, in the left-hand side menu, select the option.
-
Click on the Create New button, and select the SSID option.
-
On the Create New SSID screen, configure the general settings:
-
In the WiFi Settings section, in the SSID field, enter the
network name that devices see when they search for Wi-Fi networks.
-
Configure the security settings:
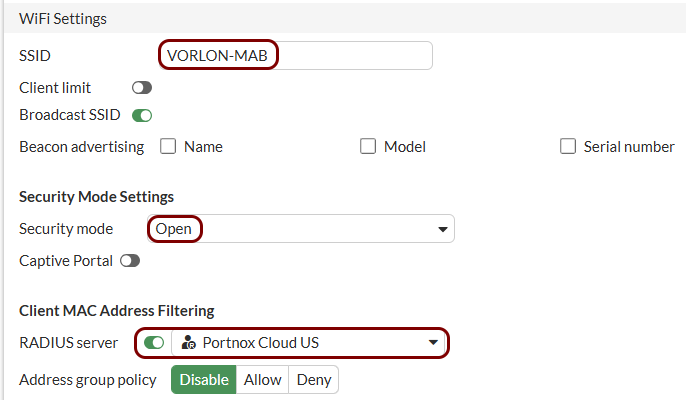
-
In the left-hand side menu, select the option.
- Optional:
Make sure that your access points broadcast the SSID:
-
Check the SSIDs column of the profile that your access points use.
If the column shows All Tunnel Mode SSIDs for each radio and you selected the Tunnel traffic mode, the access points broadcast the SSID automatically. In this case, skip the next step.
-
Otherwise, double-click the profile. For each radio, in the SSIDs field, select
the Manual option, and select the SSID that you created. Then, click on the
OK button.
Note:The Manual option replaces the automatic list of SSIDs. Also select all other SSIDs that the radio must broadcast.
-
Check the SSIDs column of the profile that your access points use.
Result: You created a separate SSID that authenticates IoT devices by their MAC address using the Portnox Cloud RADIUS server on the basis of MAC-based accounts.
Optional: Create an SSID for IPSK authentication
This is an optional task. Follow this task only if you want to authenticate devices using RADIUS-based identity pre-shared keys (IPSK). FortiGate calls this feature MPSK (Multiple Pre-Shared Keys). Skip this task if you do not need IPSK authentication.
For more information about IPSK in Portnox Cloud, see the following topic: Create a MAC-based account.
-
In the FortiGate web interface, in the left-hand side menu, select the option.
-
Click on the Create New button, and select the SSID option.
-
On the Create New SSID screen, configure the general settings:
-
In the WiFi Settings section, in the SSID field, enter the
network name that devices see when they search for Wi-Fi networks.
-
In the Security Mode Settings section:
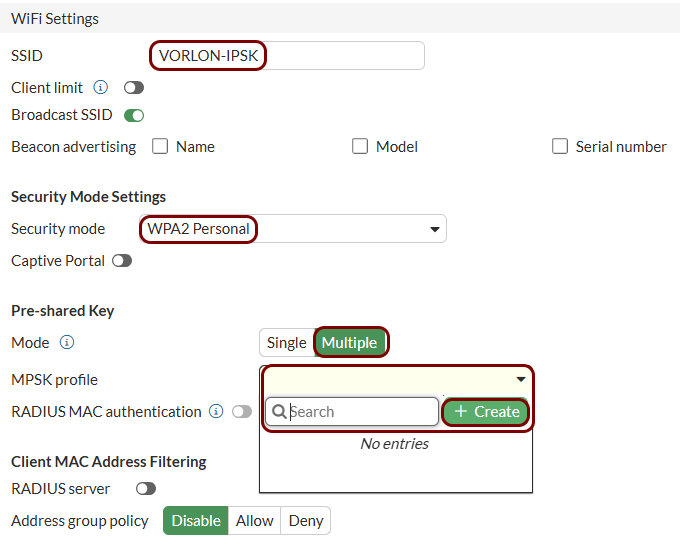
- In the Security mode field, select the WPA2 Personal option.
- In the Pre-shared Key section, in the Mode field, select the Multiple option.
- In the MPSK profile field, click on the Create button.
-
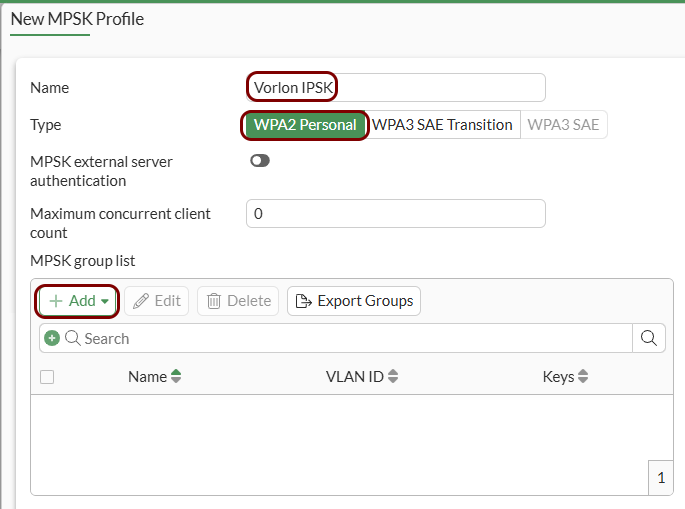
In the New MPSK Profile pane, configure the MPSK profile:
-
In the New MPSK Group pane, configure the MPSK group:
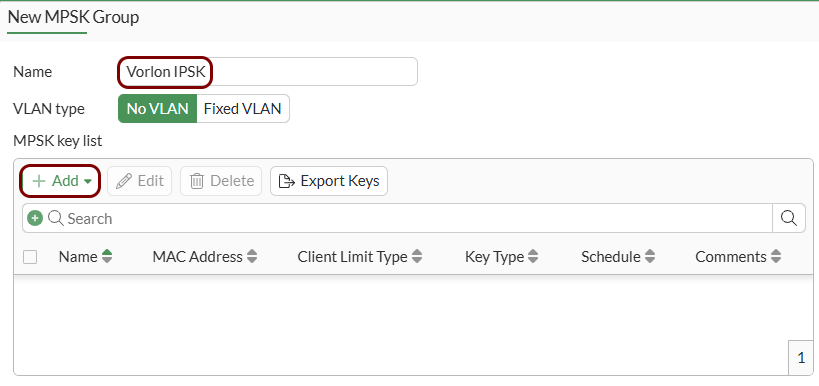
- In the Name field, enter a name for the group.
- In the VLAN type field, leave the No VLAN option selected.
- In the MPSK key list section, click on the Add button.
-
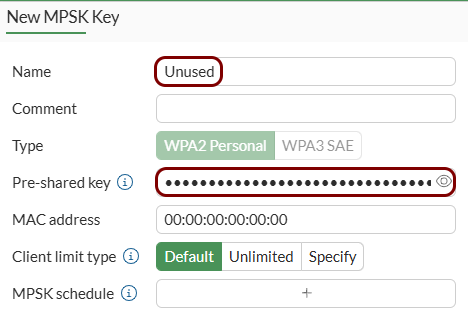
In the New MPSK Key pane, configure the MPSK key:
Note:Devices get their keys from Portnox Cloud and never use this key. The FortiGate requires it only to save the MPSK profile.
-
Configure RADIUS authentication:
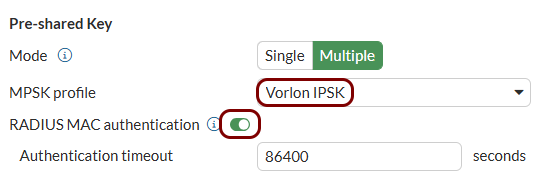
-
In the left-hand side menu, select the option.
- Optional:
Make sure that your access points broadcast the SSID:
-
Check the SSIDs column of the profile that your access points use.
If the column shows All Tunnel Mode SSIDs for each radio and you selected the Tunnel traffic mode, the access points broadcast the SSID automatically. In this case, skip the next step.
-
Otherwise, double-click the profile. For each radio, in the SSIDs field, select
the Manual option, and select the SSID that you created. Then, click on the
OK button.
Note:The Manual option replaces the automatic list of SSIDs. Also select all other SSIDs that the radio must broadcast.
-
Check the SSIDs column of the profile that your access points use.
Result: You created a separate SSID that authenticates devices using identity pre-shared keys from Portnox Cloud.
Legacy setups
The following section applies only to older Fortinet setups.
FortiWLC
The following is a configuration process for the FortiWLC series of controllers, based on FortiWLC 50D with FortiOS 8.3.
-
In the FortiOS web interface, navigate to , and click on Add to add a RADIUS server.
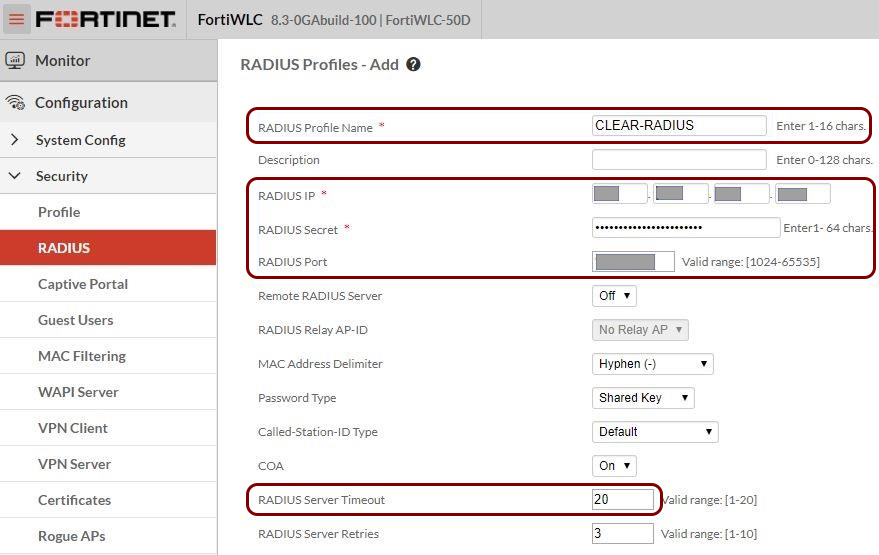
- Specify a RADIUS Profile Name for the RADIUS server.
- Set the RADIUS Server Timeout to 20 seconds.
- Enter your Cloud RADIUS details.
-
Navigate to , and click on Add to add a RADIUS accounting server.
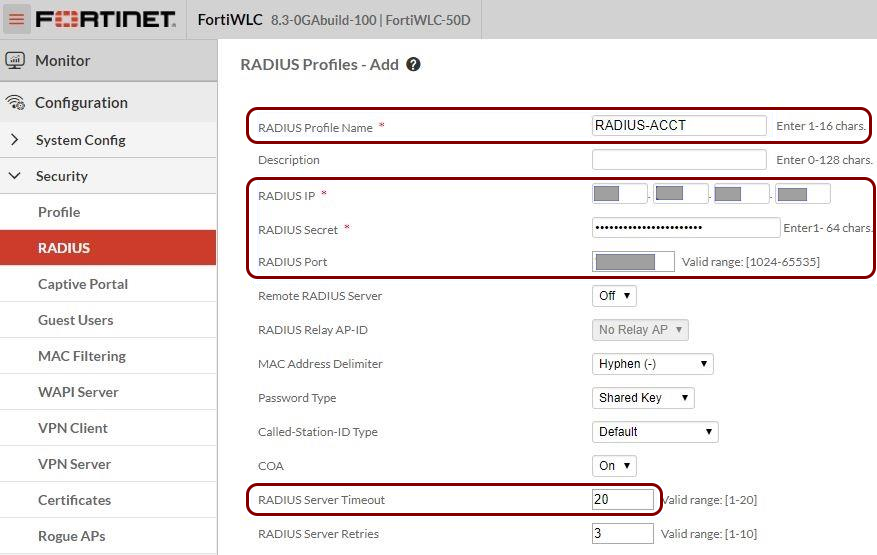
-
Navigate to , and click on Add to add a new security profile.
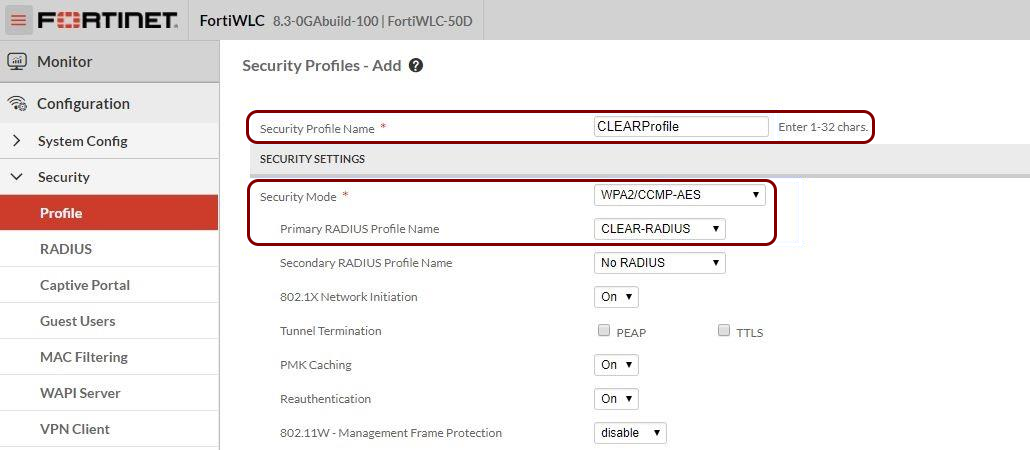
- Specify a Security Profile Name.
- In Security Mode, select WPA2/CCMP-AES.
- In Primary RADIUS Profile Name, select the RADIUS server that you created in previous steps.
-
Navigate to , and click on Add to add a new ESS profile.
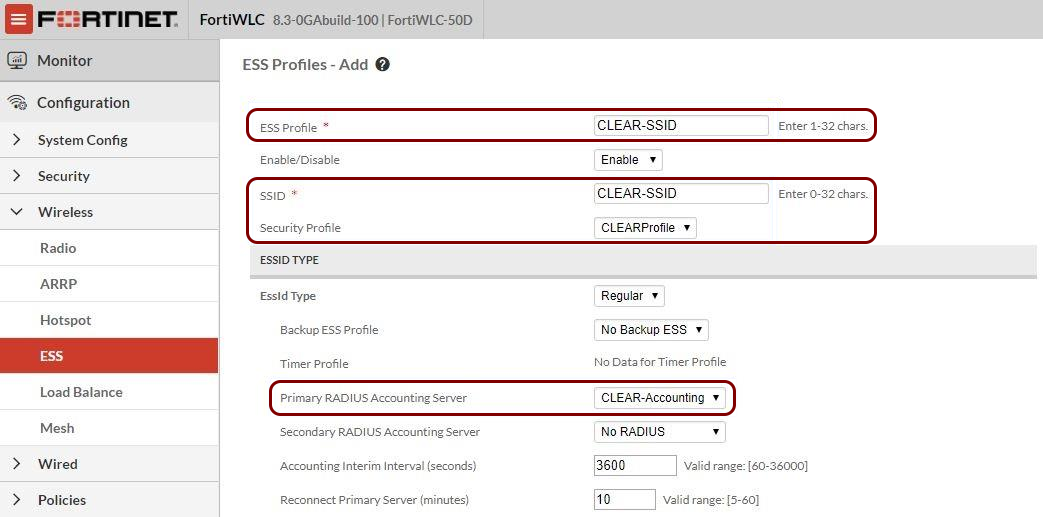
- In ESS Profile, specify a name for the ESS profile.
- In SSID, specify the WLAN SSID.
- In Security Profile, select the security profile you created in previous steps.
- In Primary RADIUS Accounting Server, select the RADIUS accounting server that you created in previous steps.